
For non-tech founders with no CTO
Your app works.Will it pass thesecurity review?
Built with Lovable, Cursor or a contractor? Before a big customer, an investor or an auditor looks at your code, we check it, tell you what they will find, and fix it. Your stack stays.
Security questionnaire
ExampleCan one customer see another customer's data?
Not sureAre API keys kept out of the code?
NoCan you restore yesterday's data?
Not sureWho has access to production?
Not sureIs every change tested before release?
No
Can you answer these today? After the Review, you can.
2 weeks
To a written verdict
Fixed price
Every step, agreed up front
Your stack stays
We fix it, we do not replace it
The product works. You just cannot prove it is safe.
Everyone who could tell you the truth about your code either built it or wants to sell you the next one.
- A big customer sent a security questionnaire, and you cannot answer half of it.
- An investor wants a technical call, and you cannot explain your own code.
- Lovable, Cursor or a contractor built it, and nobody senior has checked it.
- A fix in one place breaks something else.
- You are not sure who can see whose data.
- Your developer is leaving, and what they know leaves with them.
AI tools write code that runs, not code that is safe
What 2026 research on AI-written code found:
44%
of coding tasks given to AI models produced code with a security flaw. In a year, the average pass rate moved from 55% to 56%.
Source: Veracode report, July 202648%
of developers always check AI-written code before they commit it, although 96% do not fully trust it. A survey of 1,100 developers.
Source: The Register, January 20266 → 35
published security flaws traced to AI coding tools: 6 in January 2026, at least 35 in March. Tracked by Georgia Tech researchers.
Source: Infosecurity Magazine, March 2026What we check
The same list a customer's security team or an investor's adviser uses.
Access control
Who can see and change whose data.
Secrets and API keys
What is exposed in the code or the browser.
Customer data walled off
Every customer's data kept apart from every other.
Backups and rollback
What happens on the worst day.
What the AI-generated parts hide
Duplicated logic, fixes of symptoms, missing tests.
Compliance gaps
SOC 2, HIPAA or GDPR, where they apply to you.
Know first. Then fix. One step at a time.
Fixed prices, agreed before each step. You decide on the next step only when the last one is done.
Risk Assessment Call
Free
30 minutes, with our lead architect
Who built the product, what must happen before your date, and what breaks today. A straight answer on whether a Review is worth your money now, including “no, not yet”.
- Your 3 biggest risks, in writing, after the call
- No preparation needed
Production Readiness Review
$4,000
Fixed price, 2 weeks, read-only
Our lead architect reads your code, cloud setup and data the way an investor's adviser or a customer's security team will. Anything critical, like an exposed key, you hear about the day we find it.
- Findings rated by business impact, with a fix estimate
- Fix-or-rebuild verdict, with the cost of each path
- A roadmap any team can carry out
- One-page summary for your investor
Harden and Take Live
From $12,000
Per milestone, fixed price
Our team makes the fixes from the roadmap, in order of risk. Our lead architect signs off each milestone. Your stack stays.
- Staging before production, rollback built in
- You approve each milestone before the next starts
- Handover docs, so any developer can run it
Retained CTO
From $5,000/mo
One day a week, or two
When the product is live and stable, our lead architect stays on as your part-time CTO: the person who owns the technical decisions.
- Weekly decision call with a written log
- Vendor work checked before every payment
- Offered after a delivered Review, never at first contact
Clear enough for you. Detailed enough for your engineers.
Each finding says what it means for your business, with the evidence and a scoped fix your developers can start on the next day. What is built well is listed too, so nobody touches it.
Production Readiness Review: findings
Example- Critical
Customer data readable without a login
One customer can see another customer's records.
Fix: 2 days
- Critical
Payment API key in the browser code
Anyone can find it and use it.
Fix: Half a day
- High
No tested way back after a bad release
A broken release means hours of downtime.
Fix: 3 days
- OK
Sign-up and payments
Built well. No reason to touch them.
Fix: None
Verdict: fix, do not rebuild. Four milestones, in order of risk.
Anything critical, like an exposed key, you hear about the day we find it. Not at the end of the two weeks.
A small senior team, led by an architect who has been through the audit
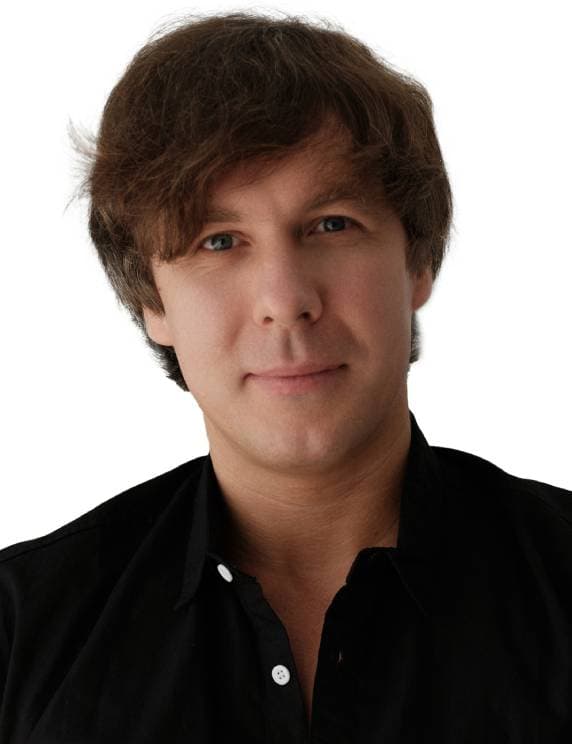
Michael Ratnikov, founder and lead architect
Michael does every Review himself and signs off every fix milestone. He has 18 years in software. He was CTO at two startups, then for five years lead architect of a US insurance platform that holds personal and health data and passed SOC 2 and HIPAA audits.
He started Softwisery in 2023 for one reason: the team that built a product cannot be its judge. Founders need someone who did not build it, and who has no rebuild to sell.
The team that makes the fixes
Michael signs off each milestone before it reaches you. You always know who is working on your product.
Ivan Navrotskiy
Engineering lead
Irina Pastushenko
Design lead
Margarita Svirina
Business analysis lead
A verdict you can trust, even when it costs us work
Most firms that review code also sell the fix, so every problem they find is work for them. We do the fixes too. These rules keep the verdict on your side. Short enough to forward to your investor.
Keeping the verdict independent
- The Review comes first, at a fixed price.
- The Review fee is not credited against later work.
- The roadmap works for any team.
- A fix before a rebuild, if it is cheaper.
Your code and data
- NDA first, before we see anything.
- Read-only access during the Review.
- For the fixes, only the access each milestone needs.
- The work stays in your accounts. Nothing is copied out.
- All our access is removed at the end.
- Our lead architect signs off each milestone before it reaches you.
Who this is for
A good fit
- A B2B product that is live, or about to be, with real customers or sensitive data.
- No CTO, or nobody senior who did not build it.
- A date: a big deal, a round, an audit or a developer leaving.
- Built with AI tools, contractors or an agency. Your own Lovable build counts.
Not a fit
- You need a certificate or a penetration test. We are neither.
- A small consumer app with no sensitive data and no deadline. A cheap automated audit may be enough.
Questions founders ask
Not on the list? Ask it on the call.
Maybe. AI tools are good at code that runs, and weak at code that is safe. The usual gaps are access control, exposed keys, customer data that is not walled off, and no way back after a bad release. The Review tells you which of these you have, and what each fix costs.
Only if a rebuild is cheaper, and the report shows the cost of both paths so you can check. The verdict is written down with evidence, not opinion.
We can do the fixes, and we say so up front. So the Review fee is not credited against any later work, and no discount pulls the answer one way. The roadmap is written so your team, a new team or ours can do the work.
The report names no people and assigns no blame. It lists fixes in order, each with a scope and an estimate, so your developers can start the next day. Your team keeps shipping during the Review.
The Review checks the same list the investor's adviser or the auditor uses. You go into that meeting with an answer you can show, not one you hope is true. Nobody can honestly guarantee the outcome of a round or an audit, and we will not.
Some of them are good, and for a small app one may be enough. Before you choose, ask three things. Who reads the code, and have they led a product through an audit themselves? Do you get a fix-or-rebuild verdict with the cost of each path? Is there a summary you can send to an investor as it is? The Review gives you all three.
If a customer contract requires it, yes. The Review does not replace it. But SOC 2 checks the process, not the architecture. With a Review first, the auditor checks controls that already work, not gaps you find during the audit.
You do not need to. The Review is read-only and runs next to your team. If your deadline falls inside the two weeks, the fixes that matter for that date come first.